Enterprise deal
The enterprise customer demands TOMs
You are about to close the contract, but the corporation’s procurement is blocking it. What is missing are verifiable technical and organisational measures (TOMs) under Art. 32 GDPR.
Technical GDPR audit for SaaS & software
Enterprise customers demand evidence. We analyse live code, architecture and third-party services — and deliver signature-ready GDPR documentation for your next audit.
As your software grows, so do the compliance requirements. We deliver the technical substance for three typical bottlenecks:
Enterprise deal
You are about to close the contract, but the corporation’s procurement is blocking it. What is missing are verifiable technical and organisational measures (TOMs) under Art. 32 GDPR.
Tender & funding
Your SaaS uses AI models or processes sensitive data. Funding bodies, investors or partners demand a well-founded data protection impact assessment.
Legal text vs. reality
Your privacy policy was reviewed by a lawyer, but in the backend an overlooked script is transmitting data to the US. We find the discrepancy before the auditors do.
You receive every document as a signature-ready final version (Markdown & PDF) — with versioning and an approval line.
We review your source code, not your pitch deck. You receive a list of concrete security gaps with the exact location.
Real-world example: We document weaknesses such as display_errors in production, missing CSRF tokens, hard-coded secrets in PHP or weak session tokens.
A catalogue of your technical and organisational measures that withstands deep scrutiny.
Real-world example: A strict table that links every measure directly to the real code location and its technical limits.
Coverage under Art. 35 GDPR for high-risk data processing.
Real-world example: We first run an evidenced threshold analysis and build a well-founded risk analysis on top of it.
The blind spot of external APIs. We inventory every real integration found in the source code, including purpose and data-transfer region.
Real-world example: In one SaaS we found 12 active external services in the code whose service descriptions did not match the signed data-processing agreements (DPAs).
Makes deletion obligations technically tangible. We build a register of all personal-data stores.
Real-world example: We reconcile existing deletion paths against gaps and verify whether connected third-party systems actually delete data on time.
Governs the safe use of AI APIs inside the company.
Real-world example: Definition of an allow/block list (what may go into external prompts?), retention periods and built-in human approval gates.
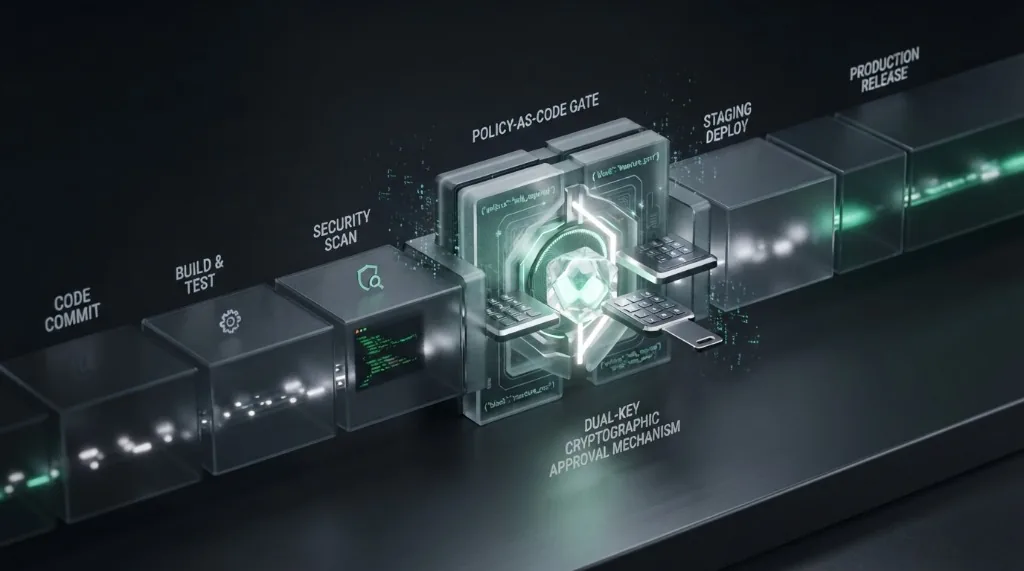
Prevents uncontrolled deployments through a runnable policy-as-code artefact.
Real-world example: Delivery of a GitHub Actions template for the two-person rule: a developer changes the code, management signs off the release.
We verify your public legal commitments against the technical reality in the backend.
Real-world example: In one case we found five hard deviations — including claimed DPAs without evidence and promised backups with no technical proof.
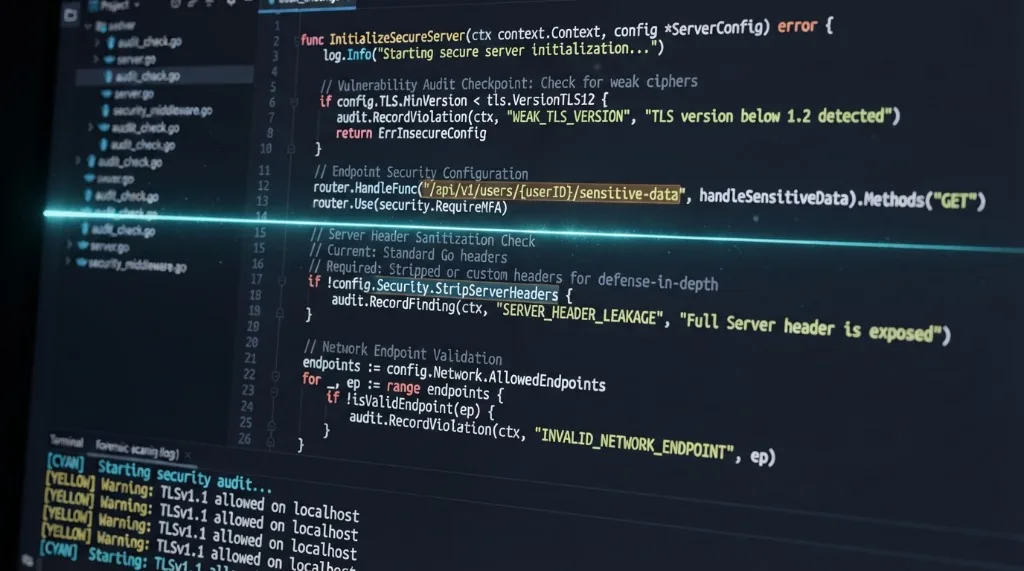
We audit the live host (HTTP headers, PHP versions, DB schema). No changes are made to your system.
We mirror the live code 1:1 and compare ZIP vs. server. Every analysis is based on the real file structure — in one case: 733 files verified as content-identical.
We strictly separate the as-is and to-be states. No figure without a source and a cut-off date. Secret values (like passwords) never end up in the documents.
You receive the final deliverable package including a manifest (SHA-256 hashes of the documents for tamper evidence) and a clear go/no-go recommendation.
We believe in hard facts. That is why we are clear about what this service is not:
This is not a SaaS tool that generates superficial PDFs in minutes. It is manual expert work on your code.
We do not issue marketing certificates. We deliver the real as-is/to-be state, name the gaps clearly and document them.
We audit the technical architecture and the code. The legally binding sign-off belongs to your management or your data protection officer (DPO).
The focus is the audit report. Remediation of the gaps found is done by your team or in a separate follow-up engagement.
Once all access and code mirrors are provided, we typically need 10–15 business days until the deliverable package is handed over.
We need read-only access to your live host, the database schema and a 1:1 export (ZIP) of the current source code.
No. We only run read-only checks and work on the provided mirror for the code inventory. Your operations keep running undisturbed.
No. A lawyer writes your privacy policy. We verify whether your software technically does what the lawyer wrote down.
You receive a fixed-price quote for the complete analysis including all 8 deliverables and the final package — scope and price are agreed transparently before we start.
Let us find out whether your software keeps what your contracts promise.
Contact: +1 (850) 273-5512 · [email protected] · MELLEPRISE LLC